Irfan Shuttari
Director of Product Management, Head of AI Strategy
AI Governance Gaps: Key Takeaways from Gartner ERAC 2026
I spent this past week on the ground at the Gartner Enterprise Risk, Audit and Compliance (ERAC) Conference, and if there was one overarching theme echo chambers couldn’t escape, it’s this: AI is everywhere, but control is nowhere.
While the majority of organizations have officially crossed the chasm to deploy AI in the workplace, compliance, risk, and security teams are now facing the hangover. We are no longer asking if we should use AI; instead, we are desperately trying to figure out how to govern the sprawl.
As I spoke with dozens of Compliance Officers, auditors, and IT leaders on the show floor, four key themes emerged that will define how we navigate the next phase of the AI revolution.
AI Sprawl is Real—and Out of Control
We have officially entered the era of "AI Sprawl". Employees aren’t waiting for corporate approval; they are actively bringing their own AI tools (BYOAI) to work.
For Compliance Officers, this has turned into a major visibility nightmare. During our session discussions, multiple leaders admitted they have no clear inventory of where AI is actively being utilized or what corporate data is being fed into external models. Security and governance were top-of-mind for every compliance leader I met, as they try to balance employee productivity with the threat of shadow AI.
The AI "Evidence Gap" Exposed
This sprawl has created a massive, systemic disconnect in corporate risk management—a theme we highlighted on stage during our breakout session.
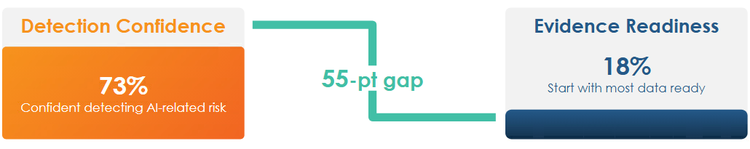
According to our latest research on the State of AI Governance 2026, 73% of organizations report that they feel confident in their ability to detect AI-related risks. However, when asked if they are operationally ready to provide hard, defensible audit evidence of that detection, only 18% can actually do so.
This critical 55-point "Evidence Gap" highlights the core of the problem: organizations are relying on optimism rather than verifiable audit trails.
Agents Are the New Knowledge Workers (Without the Rules)
Autonomous AI agents are rapidly taking over workflows once handled entirely by human employees. They make decisions, analyze sensitive data, and automate actions. Yet, organizations are failing to apply the same regulatory rules to these digital entities.
One Risk Director from a large financial institution shared a telling example with me:
"If a human employee mishandles customer data, we have clear disciplinary and audit policies. But when our new autonomous customer service agent hallucinates or accesses restricted records, who is held accountable? Who reviews the agent's logic?"
If an agent is acting as a knowledge worker, it must be subject to the same compliance, training, and operational guidelines as any human employee.
This governance challenge is further complicated by the rise of MCP (Model Context Protocol)—the technical protocol allowing these agents to connect directly with and execute changes in core enterprise systems. Speaking with a General Counsel from a major financial services firm, he shared how his team is using classification to combat the lack of visibility around these connections:
"We aren't trying to block AI; we are trying to map it. We are implementing classification policies specifically designed to flag suspicious activity when using AI tools to fully understand how AI is used in our company. If we can't flag and classify those data transfers in real-time, we can't truly understand how AI is being used across our company."
Data Remains the Ultimate Barrier
You cannot have clean AI outputs with dirty data. Bad, disorganized, and siloed data remains the single largest barrier to efficient, safe, and accurate AI usage.
Many attendees discussed how data fragmentation makes it nearly impossible to prevent models from generating inaccurate results or accessing unauthorized internal documents. Before we can trust AI to give us the right answers, we must first master our data compliance and lifecycle management.
Regulated Industries Need an "AI Audit Trail"
AI adoption is rapidly normalizing, which means we must treat AI interactions with the same level of scrutiny we apply to other critical business operations.
For highly regulated industries like healthcare and finance, this is non-negotiable. If you operate in these spaces, you need robust documentation, ironclad accountability, and a pristine audit trail around every prompt, response, and decision made by an AI model.
Let’s Continue the Conversation
The transition from AI adoption to AI governance is the defining challenge of 2026. If you’re struggling to build a defensible audit trail or contain AI sprawl within your organization, you are not alone.
Let’s connect! Schedule a brief sync with our team. We’d love to share how we are helping enterprises establish visibility, enforce strict data boundaries, and automate AI compliance.